

Server Security Hardening: Best Practices to Protect Your Infrastructure in 2027
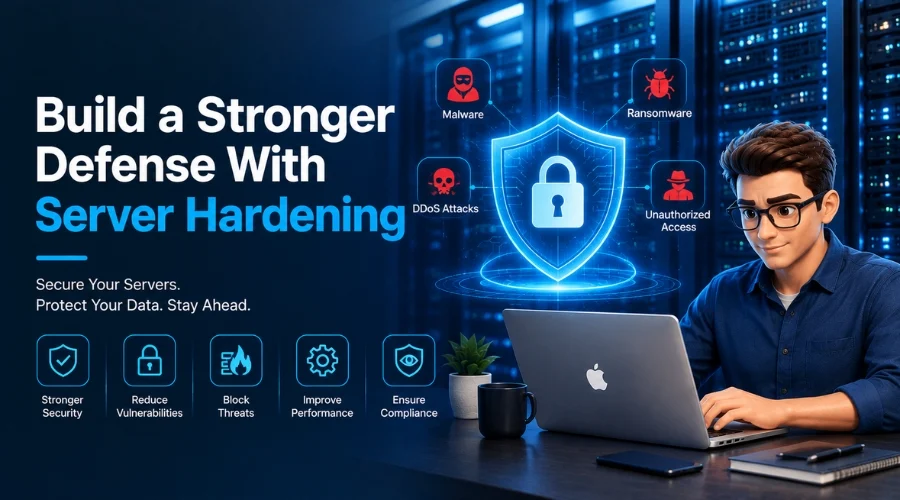
Server security hardening is the process of strengthening your server by systematically configuring it, applying updates, limiting unnecessary access, disabling unused services, and minimizing vulnerabilities to malware and other cyber threats.
In 2027, it’s increasingly non-negotiable for businesses, as they rely on digital infrastructure and a single slip can cause major damage and revenue loss.
One research report found 12,195 breaches worldwide, increasing from 20% to 34% in the previous year. These highlights show why strengthening security becomes increasingly important today.
This piece helps you understand server security hardening, how it differs from system hardening, its benefits, and the processes you can use to strengthen your servers.
Key Takeaways:
- Server security hardening is a best practice for securing your infrastructure.
- Server security hardening and system hardening are similar, but are not the same.
- Server security hardening helps prevent downtime and reduce infrastructure-sharing risks.
- Methods like patching, SSH lockdown, least privilege access, and hardening network perimeters help reduce breaches and misconfigurations.
- Businesses must invest in server security maintenance practices to protect their systems.
Is Server Security Hardening the Same as System Hardening?
Many people assume system hardening is the same as server security hardening. Yes, they’re quite similar, but not exactly the same.
System hardening means configuring your system tightly so that, once an attacker gets in, they can’t accomplish their goals. An IT team follows a structured process to harden systems by using the following approaches:
- Patching.
- Network configuration.
- User account management.
- And log checks.
It mostly focuses on the entire computing system. This includes operating systems, applications, endpoints, and configurations, basically securing the underlying systems, without contributing to server security.
Server Security Hardening Vs. System Hardening: A Quick Glance
| Aspect | Server Security Hardening | System Hardening |
|---|---|---|
| Scope | Focuses specifically on physical, virtual, or cloud servers | Covers servers, workstations, endpoints, operating systems, and other systems |
| Primary focus | Protecting server workloads, services, data, and network interfaces | Reducing vulnerabilities across a broader computing environment |
| Typical controls | Secure ports, SSH/RDP access, server permissions, service configuration, firewall rules | OS configuration, application controls, endpoint settings, user privileges, and security policies |
| Network exposure | Particularly important because servers often provide externally accessible services | Considered, but varies depending on the system being hardened |
| Availability | Strong emphasis because server downtime can affect business services | Depends on the type of system and its role |
| Relationship | A specialized application of system hardening principles | The broader security practice |
In simple terms, server security hardening is a subset of system hardening. Many methods are similar in both of the approaches. But one mainly focuses on servers, and the other on the underlying system.
Why Does It Matter in 2027?
Cybersecurity threats are increasing faster than ever. In 2027, they will reach sky-high levels. Reports show nearly 31% of cyberattacks stem mainly from software vulnerabilities. That’s why you can’t take cybersecurity hardening lightly. This process becomes mandatory for reducing downtime, compliance fines, operational costs, and reputational damage is now mandatory.
Learn why cybersecurity hardening becomes the primary goal for businesses:
Escalating Threats
AI bots can even break into the most complex systems. So, focusing only on regular updates isn’t enough. Businesses should think of other stronger escapes to strengthen their servers- this is where the server maintenance checklist stands.
Breach Costs Keep Rising
A relevant IBM report confirms that average breaches worldwide climbed to $4.44 million in 2025. The U.S. tops the list, hitting a record of $10.22 million in breaches.
Downtime Costs Keep Climbing
Research found that hourly downtime now costs more than $300,000 for 93% of businesses, and high-impact outages can reach $2 million an hour.
Patch Backlogs Keep Growing
On average, 779,935 vulnerabilities remain inside organizations’ systems. Among them, 28% remain unpatched even after 6 months. That leaves more than 57,000 known problems open, according to a recent survey.
Cloud Misconfigurations Drive Failures
Nearly 73% of organizations use a hybrid cloud setup, but cloud security fails in 99% of cases because of preventable misconfigurations that hardening can easily prevent.
Shared Infrastructure Risks
In a cloud hybrid model, multiple customers share a single resource. Poor configuration welcomes security issues into your system. This is why strengthening your server becomes crucial.
How Can You Harden Your Server Security?
Don’t wait for server crashes, mounting security alerts, system slowdowns, and more suspicious login attempts. Hire dedicated DevOps engineers or cloud specialists for AWS, Azure, or Google Cloud, and strengthen your server before its performance goes down the drain.
Follow these moves to harden your infrastructure the right way:
Enforce Least-Privilege Access
Restrict most users’ permissions and grant access only for core operations. Disable the default accounts and enforce MFA for admins. You also need to limit lateral movement within the systems. Ransomware attacks increase when attackers use compromised data in 23% of cases.
Automate Patch Management
Make it a rule to install critical security updates automatically within 72 hours. Patching is one of the best system hardening practices and solves many common server problems. Unpatched flaws increase malware attacks by up to 32%.
Harden Network Perimeters
The network perimeter is the gateway to your server. Use a firewall to block every incoming connection. Also put focus on closing internal network ports and services because every opening gives a path to the attackers to invade the system.
Lock Down SSH & Remote Access
SSH allows administrators to access and manage servers remotely. Use SSH keys for strong protection. Also disable root logins and limit connection attempts. You may use non-default ports to reduce automated scanning. You can allow remote access by restricting it to trusted IP addresses or specific locations.
Deploy Continuous Monitoring
Security hardening only pays off when you constantly monitor the flaws by enabling audit logging and integrity checks (AIDE/Wazuh). A Gartner report shows that catching misconfigurations early can reduce cloud failures by up to 99%.
Key Note:
You can also strengthen your CI/CD pipelines by applying step security harden runner practices. This process may include isolating build environments, rotating secrets automatically, scanning dependencies for known CVEs before deployment, and limiting access to production systems to authorized users only. This prevents supply-chain attacks that target build systems to inject malware into production artifacts.
Closing Thoughts
Businesses these days aren’t investing in cybersecurity hardening without a reason. They know it can help prevent downtime and avoid heavy compliance penalties. Hardening practices can also avoid costly breaches and reduce shared infrastructure risks.
Don’t wait for your server crash; start implementing these server security hardening steps from day 1 to stay protected from threats. If you’re wondering where to fortify your infrastructure, then contact The Tech Clouds (TTC). We offer end-to-end server management services, starting from hardening and monitoring to 24/7 incident response.
Partnering with us means investing in growth, not glitches. Let’s secure your servers together.
Frequently Asked Question
How often should I patch my servers?
Apply patches within 72 hours; don’t wait months or years. CIS guidance recommends addressing critical issues within 14 days.
Is SSH key authentication enough?
SSH isn’t enough. You should pair it with strong MFA, rate-limiting, non-root logins, and hardened network perimeters.
What tools help monitor hardening compliance?
For hardening monitoring, many tools are available, but top defenders include AWS Config and AWS Security Hub for AWS environments. Microsoft Defender for Cloud and Azure Policy for Azure. And Security Command Center and Cloud Asset Inventory for Google Cloud.
Can hardening cause downtime?
Yes, it may cause problems if changes aren't tested first. Always validate in pilot systems and document rollback steps before broad rollout. You can also partner with The Tech Clouds (TTC) to avoid these risks.
Recent Posts
Related Blogs
High CPU Usage on Your Server: Causes, Diagnosis, and Fixes
Suddenly your server feels sluggish? You have seen all requests timing out, and the dashboard showing a red signal screaming: CPU at 100%. Do you know what that sign means...
Why Does My Server Keep Crashing? Common Causes and Fixes
Has your server crashed in the middle of a critical deployment, taking your uptime, your revenue, and peace of mind with it? You’re not alone. Every year, businesses lose thousands...
Common Server Problems and How to Fix Them: The Complete Guide
KeyTakeaways Most slowdowns occur when CPU stays above 90%, and disk I/O wait exceeds 10–20ms. Focusing on DNS authentication and strengthening firewall rules can prevent network hiccups, which are a...
How The Tech Clouds Built a Smarter Website & Server Monitoring Solution
Your website looks nice; nothing felt off. The server seems to be up; who knows? But then you wake up at 2 AM to check whether everything runs as you...
What Is The Difference Between Cloud Computing and Cloud Migration?
Businesses today aren’t just building in the cloud; they are constantly rethinking where and how their systems run. That’s where the concept of cloud migration comes in: moving your on-premises...
Server Monitoring vs. Server Management: What’s the Difference?
Server monitoring vs. server management is one of the most confusing topics. Business owners think that they need only one approach to run their websites, email, and apps through servers....
Common Cloud Migration Mistakes and How to Avoid Them
Businesses need fast, efficient, and secure systems in today's time. However, 70% face delays, cost overruns, or performance issues, even when cloud migration is done by experts. This is because...
Cloud Migration Checklist – An Ultimate Guide
Switching to the cloud is one of the most preferred choices of modern businesses. This strategy streamlines their workflow and provides flexibility and scalability. With a cloud computing strategy, remote...